Information Security Management System
Protecting information through structured processes
We have implemented an Information Security Management System (ISMS) in accordance with ISO/IEC 27001:2022.
ISO/IEC 27001:2022 addresses information security, cybersecurity and privacy protection and provides a systematic framework for managing information security risks and protecting information within an organization.
As a Regulatory Affairs and Quality Management service provider, ELLECOM regularly works with information and documentation entrusted to us by manufacturers, customers, partners and other stakeholders. Protecting the confidentiality, integrity and availability of information is therefore an important part of our organizational processes.
Our Information Security Management System provides a structured approach to identifying and addressing information security risks and continuously reviewing and improving our information security practices.
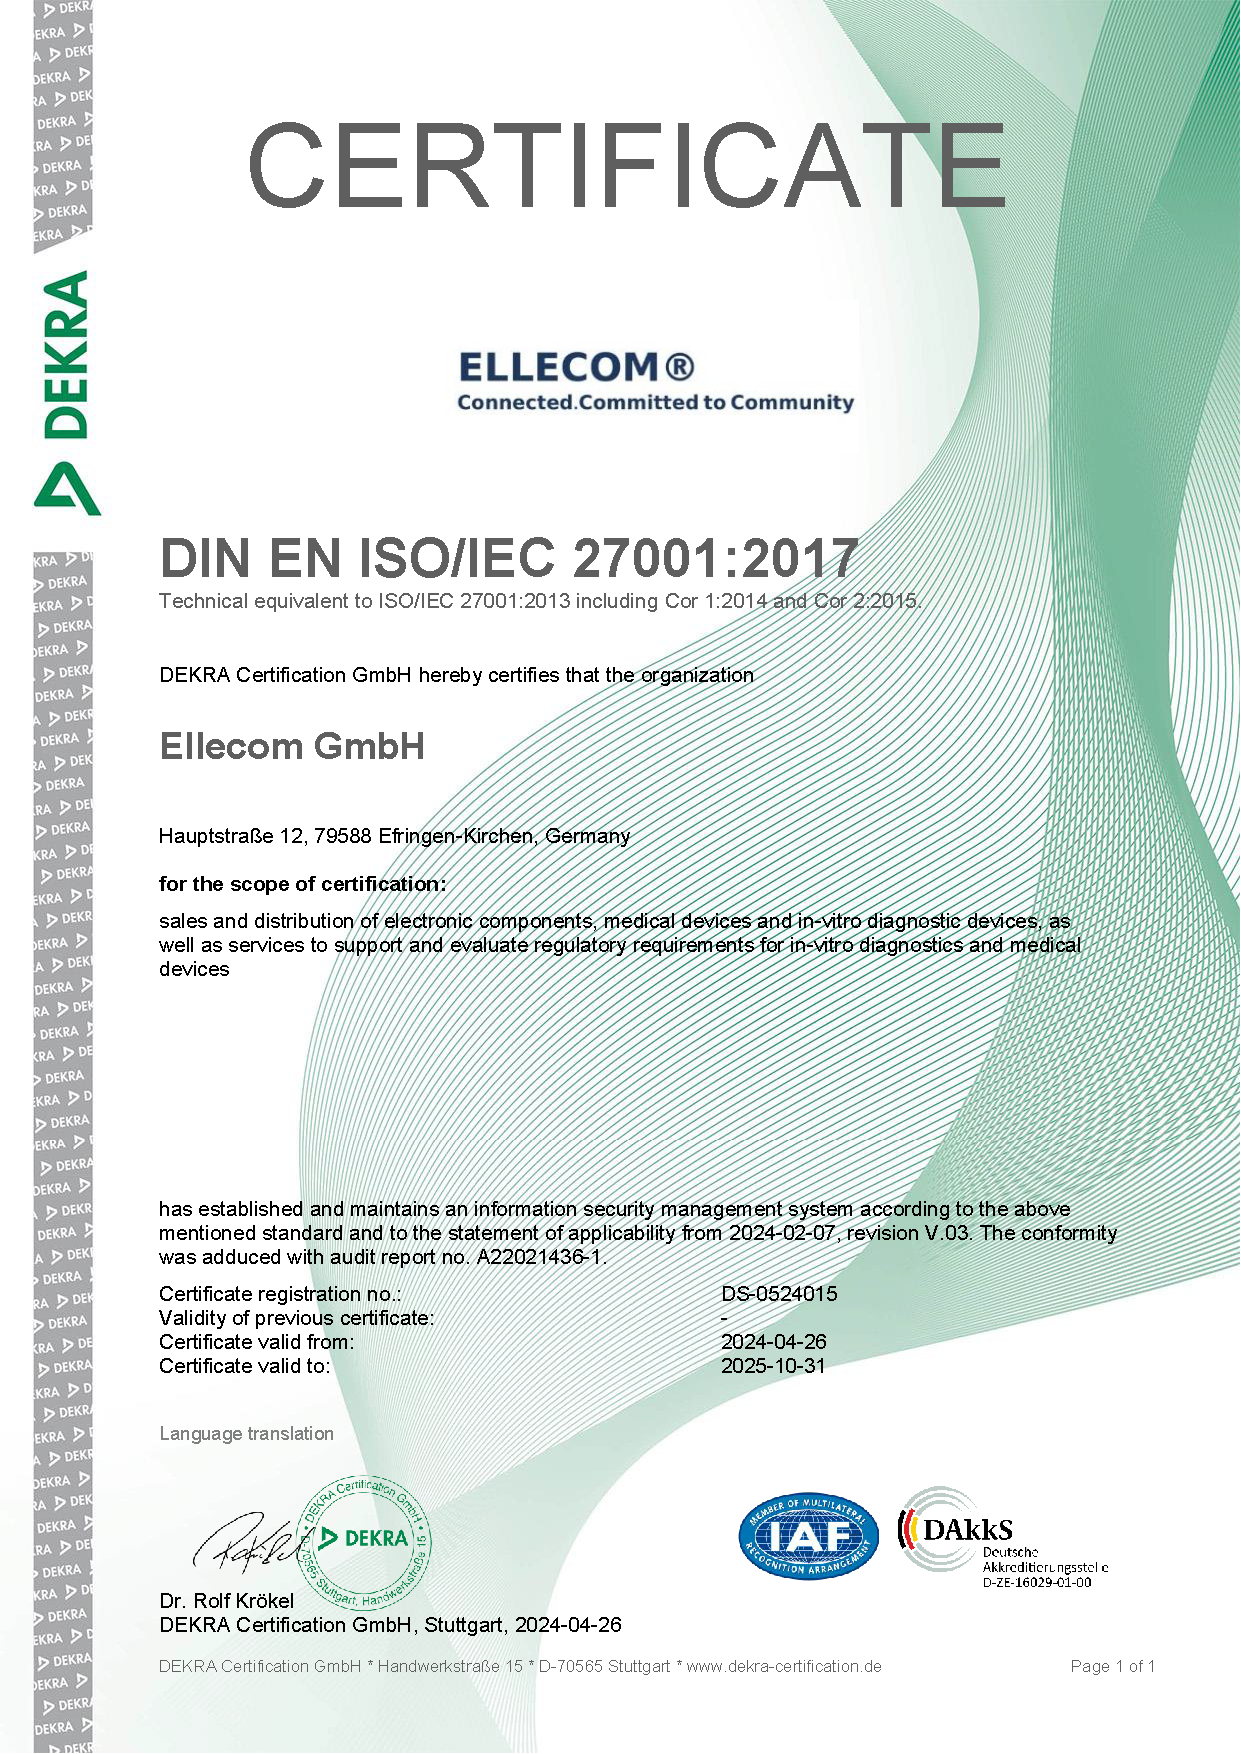
ELLECOM previously underwent a voluntary independent certification process with DEKRA, during which our Information Security Management System was externally audited against the applicable ISO/IEC 27001 requirements.
This experience continues to support our approach to information security today, while our ISMS has been implemented in accordance with ISO/IEC 27001:2022.
Confidentiality. Integrity. Availability.
Confidentiality - Protecting information
Information is protected against unauthorized access, disclosure and misuse.
Integrity - Preserving the reliability of information
Information is maintained accurately and completely and protected against unauthorized or unintended modification.
Availability - Information when it is needed
Information and systems remain accessible to authorized users when required.